Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

How to Secure Agentic Coding Tools: Cursor and Claude Code

Cursor and Claude Code now read source code, install packages, and push commits with much of the access a senior engineer has, and often with less oversight. Give an agent a prompt to fix a bug, and it may pull a private API key from a config file, pass a customer record into its context window, or send a snippet of proprietary logic to a third-party model provider to reason about the fix. Security teams built policy for developers typing code by hand.

Assessing Third-Party AI Vendor Risk Before It Becomes a Problem

Every SaaS tool your organization onboards now carries a hidden layer of AI risk. The chatbot on your CRM, the transcription service your sales team runs, the code assistant embedded in your IDE. Each one processes company data through models you did not build, in ways your vendor questionnaire was not written to catch. Traditional third-party risk management was designed to evaluate infrastructure, access controls, and data handling.

How agentic AI works inside your tools: A practical example with Acronis Service Desk

Author: Alexander Ivanyuk, Senior Director, Technology For many MSPs, AI still looks like an extra tool outside the real workflow: open a chatbot, paste in a ticket, ask for help, copy the answer back and continue working. It may save a few minutes, but it also creates more steps and more places where context can be lost.

Monitoring AI Agent Behavior in Production

Monitoring AI agents in production is a fundamentally different problem from monitoring traditional software or even generative AI models. Because agents run autonomously, chain multi-step reasoning across tools and systems, and change behavior as their underlying models evolve, standard software metrics like uptime and CPU utilization miss almost everything that matters. ‍

Cloudflare AI Search: give your agents a search engine for your data

Today, we’re excited to announce a few developer experience improvements to Cloudflare AI Search to make it easy to manage a search solution out of the box. Previously, you had to stitch together components of the Cloudflare primitives (Workers AI, AI Gateway, Vectorize, R2, Browser Run) but now, AI Search can do this automatically, and better. Our goal is to give your agents their own search engine, where they can easily find data to provide better answers for themselves and their humans.

How to Build a Durable AI Governance Program: A 3-Pillar Framework

AI adoption inside the enterprise has outpaced the governance built to contain it — 57% of employees have used AI tools for work without telling their manager. Policies get written and committees get formed, but exposure keeps accumulating, because data governance, AI oversight, and security are almost always run as three separate programs. In this video, Kovrr breaks down the three pillars that need to connect, and what separates a durable AI governance program from a documented one.

Securing Agentic AI Workflows in n8n: From Leaked API Keys to Encryption Key Compromise

A leaked n8n API key is only the start. GitGuardian's research traces the full chain, from exposed tokens and weak keys to CVE-2026-25053 and the N8N_ENCRYPTION_KEY that protects every stored credential, then lays out a hardened configuration to break it.

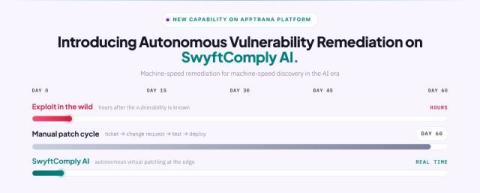
SwyftComply AI: How We Turn Vulnerability Flood Into Audit-Ready Protection

For the last several months, we have run AI agents against real production applications across industries. Two questions drove the work: what does AI-powered vulnerability analysis and pentesting surface at scale, and what does protection have to look like to keep pace. The vulnerability discovery side confirmed what Mythos made impossible to ignore.