On March 29, a massive supply chain compromise in 3CX software resulted in malware being installed globally across multiple industries. It is similar to the other high-profile supply chain attacks (like SolarWinds and Kaseya) in that rather than targeting a single organization, the criminals target a popular service or software provided to many large organizations. With one single compromise of the supplier, dozens and potentially hundreds of organizations may fall in turn.
Banks are entrusted with a great deal of personal information, money, and more by their customers. When a bank isn't able to secure those things, it's a major issue. This is an issue that the Tri-Counties Bank in Chico faced earlier this year. It wasn't money that the bank failed to protect, but customer information. The bank suffered from a serious cyber attack and lost confidential information in the process.
We will continue to update on this dynamic situation as more details become available. CrowdStrike’s Intelligence team is in contact with 3CX. On March 29, 2023, CrowdStrike observed unexpected malicious activity emanating from a legitimate, signed binary, 3CXDesktopApp — a softphone application from 3CX. The malicious activity includes beaconing to actor-controlled infrastructure, deployment of second-stage payloads, and, in a small number of cases, hands-on-keyboard activity.
Over the past 24 hours, Cloudflare has observed HTTP DDoS attacks targeting university websites in Australia. Universities were the first of several groups publicly targeted by the pro-Russian hacker group Killnet and their affiliate AnonymousSudan, as revealed in a recent Telegram post. The threat actors called for additional attacks against 8 universities, 10 airports, and 8 hospital websites in Australia beginning on Tuesday, March 28.
The details in this thwarted VEC attack demonstrate how the use of just a few key details can both establish credibility and indicate the entire thing is a scam. It’s not every day you hear about a purely social engineering-based scam taking place that is looking to run away with tens of millions of dollars. But, according to security researchers at Abnormal Security, cybercriminals are becoming brazen and are taking their shots at very large prizes.
A new report from ENISA, the European Union Agency for Cybersecurity, looking at cyberattacks targeting the European transport network over a period of almost two years, has identified that ransomware has become the prominent threat. ENISA's report, its first ever analysis of the myriad of cybersecurity threats facing the transport sector in the EU, mapped and studied cyber incidents targeting aviation, maritime, railway, and road transport between January 2021 and October 2022.
The other week, BitSight published research identifying thousands of organizations using internet-facing and exposed webcams with many video and audio feeds susceptible to spying. The potential consequences are serious – an attacker could potentially view private activities and eavesdrop on sensitive conversations, presenting a variety of privacy and security concerns. Below are some of the screenshots BitSight captured from exposed devices (blurred for privacy).
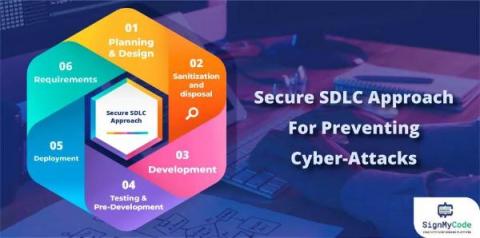
According to CrowdStrike Report, a 50% increase has been analyzed in active intrusions and cyber-attacks in 2022. And the number may increase in 2023 too. With more and more applications becoming a target of hackers, it getting complex for developers to identify relevant security approaches. Development teams are somewhere unable to select the best mechanism, which would be compatible, high-performing, and strong enough to prevent attacks.
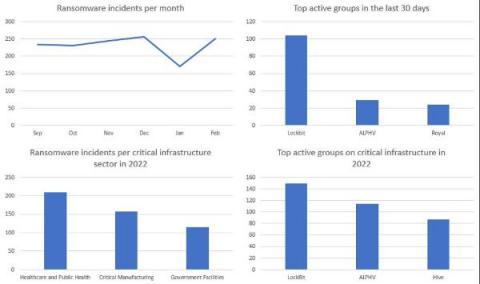
In our new threat briefing, Forescout’s Vedere Labs details tactics, techniques and procedures (TTPs) commonly adopted by ransomware groups and provides specific mitigation recommendations. In addition to basic cyber hygiene practices, we recommend using Forescout XDR for extended detection and response. Its 1,500+ detection rules cover hundreds of the TTPs most commonly used by ransomware.
Cross-site request forgery (CSRF) attacks are a form of cyberattack from malicious websites, emails, blogs, instant messages, or applications. This type of attack tricks the user's web browser into executing an unwanted action on a secure website. Browsers typically attach session cookies when making a request to a website. Thus, it becomes difficult for the site to differentiate between legitimate requests that are authorized and forged requests that have been authenticated.
Malicious packages are often spread by the open source NPM and PyPI package repositories, with few other repositories affected. Specifically – there was no public evidence of severe malicious activity in the NuGet repository other than spam packages used for spreading phishing links. As with other repositories, the JFrog Security Research team regularly monitors the NuGet repository for malicious packages, including manual analysis of suspicious code.
The Minneapolis public school district includes approximately 100 primary and secondary public schools. Between the many different schools, approximately 36,000 students are served by about 1,500 teachers. The district is currently suffering from a ransomware attack supposedly and is being extorted for a $1 Million payment by a ransomware gang.
A major logistics company was hit by a ransomware attack at a time when it was reviewing and upgrading its cybersecurity defense. Kroll provided seamless incident response to enable the company to act quickly to mitigate and minimize the damage caused by the attack. The company also deployed Kroll Responder, Kroll’s award-winning Managed Detection and Response (MDR) solution, giving it comprehensive 24/7 visibility and management of threats and enhancing its long-term cyber resilience.
CrowdStrike has discovered the first-ever Dero cryptojacking operation targeting Kubernetes infrastructure. Dero is a relatively new and privacy-focused cryptocurrency that uses directed acyclic graph (DAG) technology to claim complete anonymity of its transactions. The combination of anonymity and the higher rewards ratio makes it potentially lucrative to cryptojacking groups compared to Monero, which is commonly used cryptocurrency by attackers or groups running miner operations.
AT&T is a massive telecommunications company with its headquarters in Dallas, Texas. The company is known as the largest telecommunications company in the world according to its revenue, and it is the third-largest mobile phone service provider in the United States. The company recently suffered an attack that exposed some of its customer data to hackers and may have put customers at risk. The attack wasn't on AT&T directly but on one of the company's external marketing vendors instead.
DC Health Link is part of the Affordable Care Act online marketplace of health insurance plans. The service provides health care to members of Congress as well as many staff members throughout Capitol Hill. This healthcare service was recently the victim of a cyber attack and suffered a serious data breach that exposed hundreds of politicians and Capitol Hill staff members.
The US Transportation and Security Administration (TSA) has issued new requirements for airport and aircraft operators who, they say, are facing a "persistent cybersecurity threat." The agency's new directive compels the aviation industry to improve their defences against malicious hackers and cybercriminals, just days after Preisdent Biden announced its National Cybersecurity Strategy that seeks tighter regulations to protect the United States's critical infrastructure.
Netskope Threat Labs is tracking a 17x increase in traffic to malicious web pages hosted on DigitalOcean in the last six months. This increase is attributed to new campaigns of a known tech support scam that mimics Windows Defender and tries to deceive users into believing that their computer is infected.
Acer is a well-known tech company that's based in Taiwan and with facilities and offices around the world. The company's main headquarters are in San Jose, California, in the United States. The company is known for engineering, technical manufacturing, and creating many products in the electronics industry today. The organization recently suffered a significant data attack that may have exposed company secrets, product keys, and many software images that could hurt the organization.
In our new threat briefing report, Forescout’s Vedere Labs provides details on the recent ransomware campaign targeting VMware ESXi virtualization servers, or hypervisors, and analyzes two payloads used in these attacks: variants of the Royal and Clop ransomware. We also present the tactics, techniques and procedures (TTPs) used by attackers in this campaign, discuss mitigation recommendations and list indicators of compromise (IOCs) that can be used for detection or threat hunting.
APIs will continue to drive business and accelerate digital transformation this year to the extent that nearly no other technology can; according to the 19th Developer Economics survey by Slashdata, almost 90% of all developers use APIs. This makes them a target for attackers who aren’t afraid to engage in any tactic, especially tried-and-true methods like parameter tampering attacks - malicious API attack traffic surged 117% from 2021 to 2022.
Crystal Bay Casino is a gambling establishment located in Lake Tahoe. The facility includes slots, table games, and sports betting and features a small hotel known as the Border House for gamblers to stay in luxury. This luxury casino was recently hit by an attack on its IT servers, and its customers may have had their confidential information exposed in the attack. Learn about the full scope of the attack and how the casino is responding to this incident to protect its customers.
Dole PLC is a massive agricultural company headquartered in Dublin, Ireland. Dole has several offices and production facilities in the United States and supplies food products in 75 separate countries. The company maintains a staff of over 38,000 employees and offers more than 300 different products throughout the world.
Address Resolution Protocol (ARP) acts as a vital bridge between the world of IP addresses and MAC addresses, allowing devices on local area networks to seek out each other's physical address based solely on their IP. ARP (Address Resolution Protocol) can also be defined as a communication protocol used to map a network layer address (such as an IP address) to a link layer address (such as a MAC address).
Willie Sutton, the criminal who became legendary for stealing from banks during a forty year career, was once asked, "Why do you keep robbing banks?" His answer? "Because that's where the money is." However, today there's a better target for robbers today than banks, which are typically well-defended against theft... Cryptocurrency wallets.
OAuth (Open Authorization) is a modern, open authorization standard designed to allow cross-application access delegation – for example, allowing your application to read data from your Facebook profile. Combined with the proper extensions, OAuth can also be used for authentication – for example, to log into your application using Google credentials. Since its first introduction in 2006, OAuth has gained tremendous popularity.
As part of a project to obtain more awareness of initial attack vectors outside of the common phishing and web application exploitation, Kroll’s Cyber Threat Intelligence team has developed a tool to enable the enhanced monitoring of the Python Package Index (PyPI) to find and obtain malicious packages that are added to it.
We all know about the attacker who leverages their technical expertise to infiltrate protected computer systems and compromise sensitive data. This type of malicious actor ends up in the news all the time. But they’re not the only ones making headlines. So too are “social engineers,” individuals who use phone calls and other media to exploit human psychology and trick people into handing over access to the organization’s sensitive information.