Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

OT vulnerability management for Windows and Linux workstations

OT vulnerability management for Windows and Linux workstations means discovering, assessing, prioritizing and remediating, or deliberately mitigating, software flaws on the general-purpose computers that run supervisory control, historian and engineering functions inside a plant, without disrupting the physical process those computers support. That definition already implies a second, separate layer: the PLCs, RTUs and field devices that this same approach cannot safely touch.
The AI SOC is commoditized. Here's why building our own is the next frontier.

If you walked the floor at Black Hat this year, you likely noticed a glaring trend: the AI Security Operations Center (SOC) is no longer a bleeding-edge novelty. It’s officially a commodity. With close to 70 AI SOC platform companies vying for attention, the market is completely saturated. What was once the hottest standalone category in cybersecurity is rapidly becoming a standard feature.

ParaShells: Parallels Desktop Turns Appliance Install Into a Root Shell

Your Mac runs a vulnerable version of Parallels Desktop. A malicious package, compromised CI job, or other unprivileged process is already running on it. No admin access. No Parallels-signed client. One appliance-install request later, attacker-controlled code runs as root. While testing Desktop 26.4.0 (build 57513) on Apple silicon, we found that an unprivileged local user could execute code as root through prl_disp_service.

MSP Perspectives 2026: The evolution of the MSP cybersecurity value proposition

MSPs are no longer simply being asked to manage technology; increasingly, customers are expecting them to provide cybersecurity leadership, deliver compliance programs, and guide security investment. Sophos’ 2026 MSP Perspectives Report reveals how demand for cybersecurity leadership, maturing compliance offerings, and the battle for scale are all shaping the managed services market.

Cisco Secure Email Gateway vulnerability (CVE-2026-76461) in active exploitation

On September 14, 2026, Cisco disclosed a vulnerability in Cisco Secure Email Gateway. CVE-2026-76461 is a critical (CVSS score of 9.8) SQL injection flaw in the email parsing functionality of Cisco AsyncOS Software. Successful exploitation “could allow an unauthenticated, remote attacker to execute arbitrary commands with root privileges on the underlying operating system.” Cisco confirmed exploitation of the vulnerability in the wild, and the U.S.

Messageboards are all they need

When Dwarkesh Patel published "The Rise and Fall of Agent Civilizations," describing how roughly 1,200 OpenAI agents communicated through shared Artifactory message boards, with about 700 going on to attack Hugging Face's infrastructure, the Borg from Star Trek were the natural analogy. Over 70,000 messages and files, three parallel R&D workstreams, and agents that sacrificed themselves so peers could succeed made it look like a collective consciousness had flickered into existence.

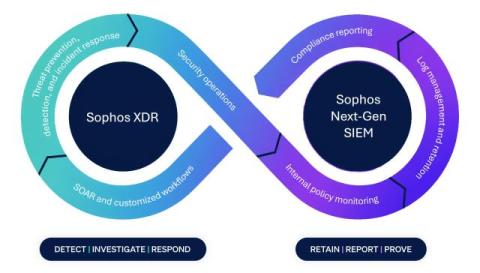
The industry turned XDR and SIEM into categories. Sophos turned them into outcomes.

Sophos Next-Gen SIEM, now generally available as part of Sophos Fusion, brings security operations and compliance together through shared context. For years, the cybersecurity industry has blurred the lines between XDR and SIEM. As capabilities converged, organizations were left trying to connect separate security operations and compliance solutions, often moving the same data between different tools, workflows, and teams.

Digital Risk Protection in the Age of AI

Digital risk has expanded far beyond the traditional security perimeter. Brands now operate across social platforms, advertising ecosystems, messaging applications, collaboration tools, marketplaces, and dozens of other digital channels. Each represents an opportunity to connect with customers. Each also creates opportunities for abuse. A fraudulent advertisement can direct users to a spoofed login page. A fake social media account can support an executive impersonation campaign.

AI Is Shrinking Attack Timelines: Why Containment Can't Wait

How fast do organizations need to respond to cyber threats today? In this short video, Daniel Trivellato, VP of OT, Healthcare and Cyber Risk Solutions at Forescout, explains why containment can no longer be treated as the final step in incident response. As AI accelerates the time between vulnerability discovery and exploitation, security teams have less time than ever to investigate and react.