Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

AI Is Reshaping Cyber Risk Faster Than Most Boards Realize

Artificial Intelligence is no longer a future cybersecurity concern. It is actively reshaping how attacks are conducted, how organizations respond, and how business leaders must think about enterprise risk. While much of the conversation around AI has focused on productivity and innovation, threat actors are already leveraging AI to make cyber-attacks faster, more scalable, more convincing, and increasingly difficult to detect.

Introducing the Cloudflare One stack: agent-powered deployment

Adopting or migrating to a Zero Trust network architecture can be a daunting task. Before a single policy changes, teams have to recall how their network is actually built: which applications exist, their authentication and authorization constructs, how traffic flows between them, and any assumptions the current architecture makes. This hands-on process requires practitioners to decode the intent behind every security and routing policy in place.

Bringing more agent harnesses and frameworks to Cloudflare, starting with Flue

2026 is the year agent harnesses go to production. The software that controls the model’s access to the outside world — harnesses like Codex, Claude Code, OpenCode, Pi, and Project Think — has matured to the point where teams are deploying agents as real, load-bearing infrastructure, not just prototypes. But building agents that survive production is hard.

1Password + Kiro: Trusted Access for AI-Powered Development

AI agents now write code, fix bugs, and ship to production. But in order to do useful work, agents require credentials. At 1Password, one of our core AI security principles is that raw credentials should never be directly exposed to LLMs, but all too often, that’s exactly what happens: most teams sacrifice security for speed and hand agents secrets in plaintext.

Aembit Extends IAM for Agentic AI to Microsoft Copilot Studio

Aembit on Tuesday announced support for Copilot Studio, extending its identity and access management capabilities to Microsoft's enterprise AI agent platform. The integration, unveiled at Identiverse 2026, gives security teams the tools to manage what Copilot Studio agents can access, under what conditions, and with a complete record of every decision. The company also released an interactive enterprise AI readiness checklist to help organizations assess their agent deployments before they go into production.

Teleport Debuts Delegated Agentic Identity and LLM Proxy in Beams Public Beta, for Containing Agents in Production Infrastructure

Two foundational identity concepts - controlling the scope of agent roles and constraining what they can access - now have a production implementation in Beams, Teleport's trusted, ephemeral agent runtime.

Agentic IAM: The Complete Guide to Identity Security for Autonomous AI Agents

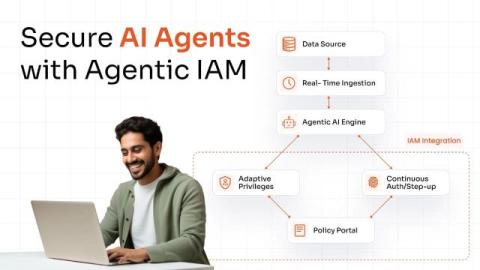
If you’ve deployed your first AI agent, then you must have given it access to your CRMs, ticketing systems, and your cloud storage. This AI agent is programmed to run 24/7, make decisions, call external APIs, and trigger actions (without a human in the loop). Now, answer these questions: If you cannot answer these questions, then you have an agentic AI identity issue. Traditional Identity and Access Management (IAM) was built for service accounts with static API keys and users with usernames.

How to build AI agents your security team will approve

A security engineer spends three weeks building an AI agent that triages phishing reports. The demo lands well. Then it hits the security review queue, and the questions start: Which tools can it call? What happens if it misclassifies? Who approves an account lockout at 2 a.m.? Where are the logs? Three more weeks pass, and the agent is still sitting in staging. This is the pattern most teams run into. The agent works, but the governance story doesn't.