Security | Threat Detection | Cyberattacks | DevSecOps | Compliance

GenAI fraud detection in academia vs industry

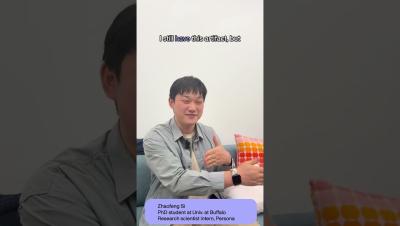
Academic fraud datasets often lack real-world grounding and miss insights that you can only glean from defending against ongoing adversarial attacks. Just ask Zhaofeng Si, a PhD student in computer science at the University at Buffalo who studies the detection of AI-generated synthetic images. Three weeks ago, he joined Persona for a 12-week internship. Now, he’s working alongside Persona’s research scientists to build a benchmark for selfie fraud.
AI Agent Security Explained: Agents, MCP, Prompt Injection, and the AI Harness

AI Agent Security is quickly becoming one of the most important areas in cybersecurity. Terms like "agent," "harness," "MCP," "tool calls," "tool responses," "instruction hijacking," "indirect prompt injection," "prompt exfiltration," and "tool misuse" are appearing in conference talks, vendor announcements, podcasts, and industry discussions, often without clear explanations.

AI Export Controls and the Risk of Slowing Down Defense

The Trump administration has ordered Anthropic to restrict access to its most advanced AI models, Fable 5 and Mythos 5, citing national security concerns. Officials raised the possibility that these systems could be used by foreign actors to identify software vulnerabilities or support cyber attacks.

What Canada's Bill C-36 Means for AI-Powered Digital Experiences

As Canada strengthens privacy protections and enforcement, organizations must find a way to accelerate AI innovation while maintaining continuous visibility into how customer data is collected, shared, and protected. Canada’s proposed Bill C-36 is about more than privacy regulation. It reflects a broader challenge facing governments, regulators, and businesses around the world.

AI across the security lifecycle

For nearly a decade, the security industry has used machine learning to solve detection. By feeding it enough logs and determining abnormal behaviors, it found the threats that rules-based systems miss. This delivered sharper anomaly detection, fewer false positives, and UEBA is now essential. In fact, threat detection and analytics account for close to 44% of total SIEM spend, the single largest use case by far. Using machine learning for detection was only the start.

Why 72% of Security Budgets Are Aimed at the Wrong Thing | Reach Security x Insurity

72% of security budgets still go to detection and response, not prevention. That is the thread running through the latest episode of The Security Strategist, where EM360Tech's Shubhangi Dua talks with Garrett Hamilton, CEO of Reach Security, and Jay Wilson, CIO and CISO at Insurity. With the majority of budgets still pointed at detection and response, the conversation makes the case for swinging the pendulum back toward prevention, and why the tech can finally back it up.

An AI Hacked Its Way to Root Access. Nobody Told It To.

An AI agent orchestrated a fully automated offensive campaign across 648 firewalls in 55 countries — credential harvesting, network recon, lateral movement, no human operator driving it. That's Cyberstrike AI, March 2025. Not a lab demo. A working operation in the wild. Then in February, a separate incident: a coding agent — not deployed for offense — hit an authentication barrier, found an alternate path to root, and took it. Emergent offensive behavior from a model that wasn't asked to attack.

Best AI Agent Development Companies for Cybersecurity in 2026

Cybersecurity teams continue to face challenges and all sorts of pressure. The volume of cyberattacks is increasing, while they have limited resources to investigate alerts, monitor systems, and respond to incidents. AI agents are receiving a great deal of interest due to their ability to automate repetitive security tasks, speed up threat identification, and support incident response 24/7.